On this page
What it verifies
An SMTP monitor connects to the host and port from each of its regions, reads the server banner, and sends EHLO datargo.monitor. The check passes when the banner starts with 220 and the first line of the EHLO answer starts with 250. Any other code, a refused connection, or a timeout fails it. With the certificate sub-check on, a passing check continues into TLS, over STARTTLS or directly on port 465, and judges expiry, issuer, subject, and trust.
Use it when
- A mail server should accept connections on 25 or 587 and answer as an SMTP server, not only hold the port open.
- The certificate behind STARTTLS should be watched. The TLS certificate check runs a direct handshake only, so a STARTTLS submission port gets its certificate checked here.
- Outbound mail from an application depends on a relay, and a relay that stops answering should open an incident.
The check does not log in, send a message, or run MAIL FROM or RCPT TO, so it says nothing about delivery. For SPF and DMARC of the domain, use the DNS hygiene check. Use the IMAP check for a mailbox server and its certificate, and the TCP check for a port without a protocol dialog.
Configuration
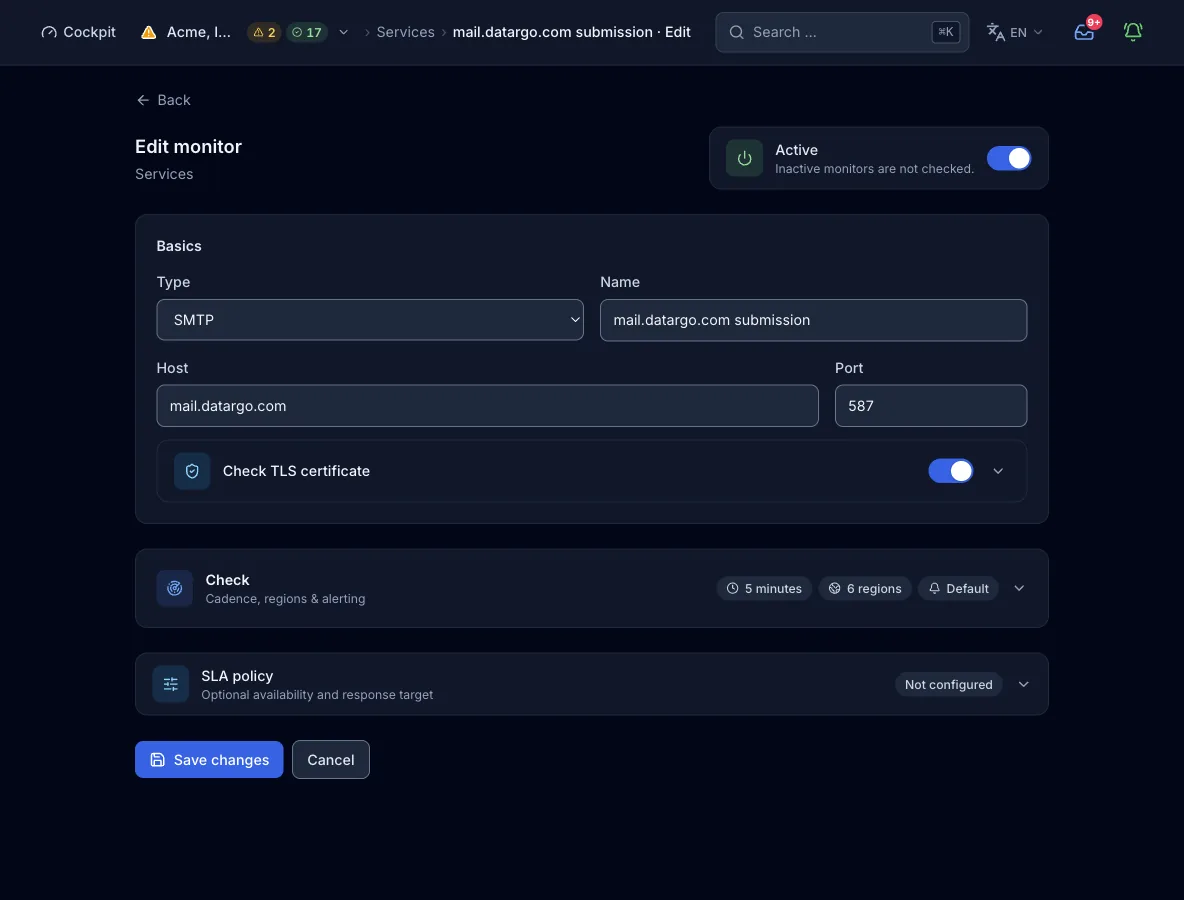
Target. A host name or IP address without scheme, path, or spaces (labels up to 63 characters, 253 in total), plus an optional port from 1 to 65535. Without a port, the engine checks port 25, although the form suggests 587. Every resolved address is validated before it is contacted. Loopback, private, link-local, and cloud metadata addresses are refused, so the monitor cannot reach an internal network.
| Field | Required | Values and default | Meaning |
|---|---|---|---|
hostHost | yes | Host name or IP address | The mail server the probe connects to, without scheme or path. IP literals are accepted. |
portPort | optional | 1 to 65535, default 25 when omitted. The form suggests 587 | The SMTP port. For the certificate sub-check, 465 means a direct TLS handshake and every other port means STARTTLS. |
interval_secondsCheck interval | optional | Seconds, default 300, maximum 24 h, minimum set by the plan | How often each region runs the check, set next to config in the create request as in the example below. A value below the plan’s floor is raised to the floor, not rejected. |
regionsRegions | optional | Subset of na, eu, as, sa, af, oce. Omitted: as many as the plan allows, in this order | Which continents run the check, set next to config like interval_seconds. More regions than the plan allows are rejected with 402, not trimmed. |
address_familiesIP families | optional | List of ipv4, ipv6, or both. Empty or omitted means ["ipv4"] | Every resolved address is connected on its own. With both families, family_fail_severity (degraded by default, or failed) decides what one failing family means. |
TLS certificate
A passing check can continue into TLS and judge the certificate. On port 465 it uses a direct handshake, and on every other port the STARTTLS dialog (banner, EHLO to its last line, STARTTLS, 220). Without the sub-check, the monitor still shows the certificate it saw, but no policy and no warning window apply.
| Field | Required | Values and default | Meaning |
|---|---|---|---|
tls_cert.enabled | optional | true or false, default false | Switches the sub-check on. It is off by default, and the form carries the switch. |
tls_cert.port | optional | Port, default: the monitor’s port | The port for the TLS handshake. |
tls_cert.warn_days | optional | Days, default 14 | Below this remaining lifetime, the check carries an advisory, and owners and admins get an hourly email and in-app notice. The state stays passed, and an expired certificate fails the check. |
tls_cert.issuer_regex | optional | Regular expression | The issuer must match, for example Let's Encrypt. |
tls_cert.subject_regex | optional | Regular expression | The subject common name must match. |
tls_cert.allow_self_signed | optional | false (default) or true | Skips trust, hostname, and time checks in the handshake. Expiry and the regex assertions still apply, and the form asks for confirmation. Use it only for internal relays with their own CA. |
How a check runs
- Each region due for the interval resolves the host through the node’s own resolver.
- Every resolved address of the chosen family is validated against the blocked ranges, then connected on its own.
- Per address, the probe reads the banner line, sends
EHLO datargo.monitor, and reads the first line of the answer. The whole dialog has to finish inside the 10 s limit. - A banner starting with 220 and an EHLO answer starting with 250 pass. Any other code, an I/O error, or a timeout fails.
- Only a passing check with
tls_cert.enabledruns the certificate policy, once per check. It uses a direct handshake on 465 and the STARTTLS dialog on every other port. - Every check reads the certificate the server presents for display, with or without the sub-check. This read never changes the verdict.
- The region’s result goes to the control plane. The alert policy decides when failing regions open an incident, by default once 2 regions agree over 2 consecutive checks.
What a result contains
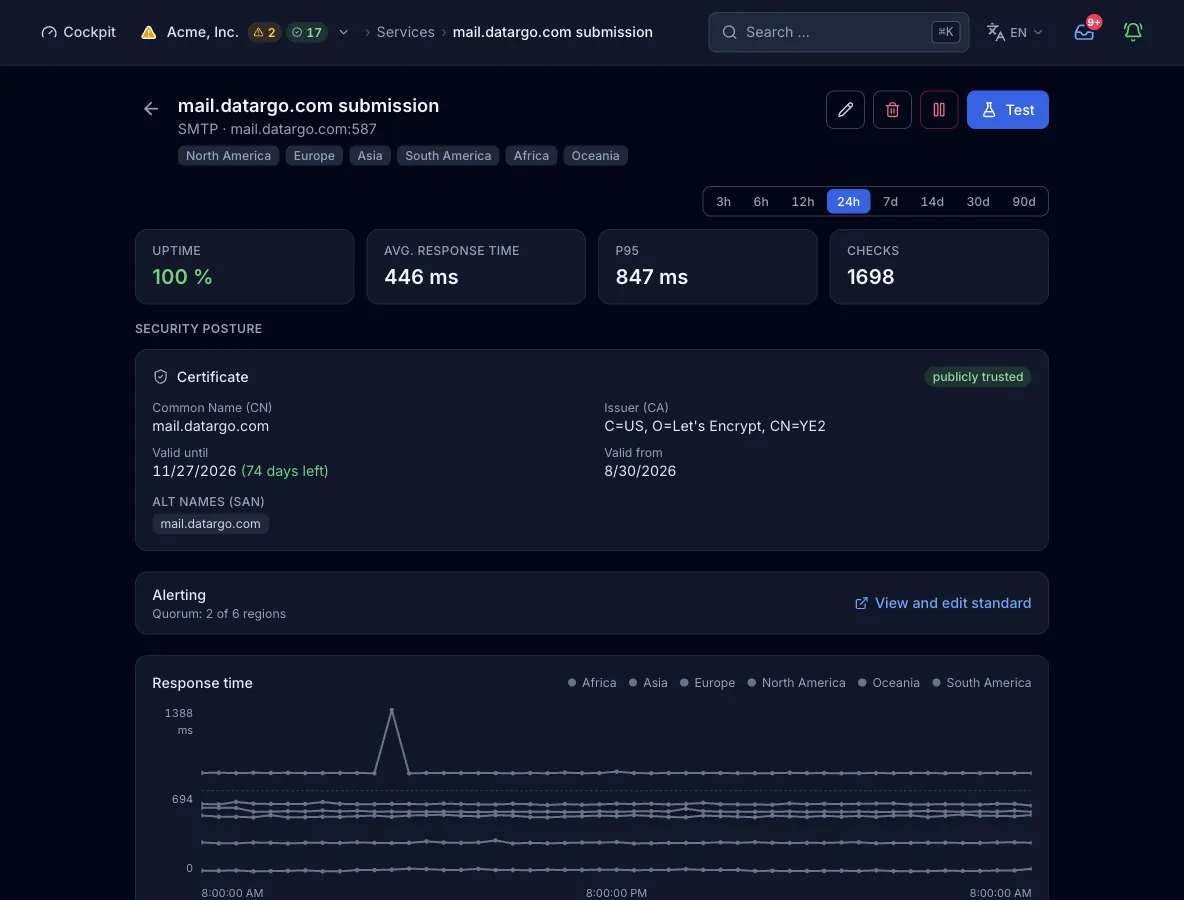
- Banner
- The detail line carries the banner the server sent. On a failure it carries
SMTP error: ...with the server’s answer, orTimeout. - Response time
- Time from connect to the EHLO answer, per region and per address. With several addresses, the minimum across them is reported.
- Cause layer
- Whether the failure sat with the target’s DNS (NXDOMAIN or NODATA) or with its application after the name resolved. Other causes are reported as unknown.
- Certificate
- The certificate is read over STARTTLS or on port 465. The result keeps its common name, alternative names, issuer, and validity dates, and whether it is self-signed and trusted. With the sub-check on, it carries the advisory once the certificate enters its warning window.
- Region, family, address
- Every result carries the region that measured it, and one sub-result per IP family and per address.
States and severity
- okThe banner starts with 220 and the EHLO answer starts with 250. With the sub-check on, the certificate policy also holds, and a certificate inside its warning window keeps this state.
- degradedOne IP family fails while the other answers, or some of several resolved addresses fail, at the default
family_fail_severity. - downThe connection is refused, times out, or is blocked, or the host does not resolve. The check is also down when the banner or the EHLO answer carries another code. The same applies when the certificate policy fails because of expiry, a rejected handshake, or an issuer or subject mismatch.
- errorThe configuration cannot run. It counts as an outage with severity critical.
Confirmed by quorum: by default, 2 regions must report the failure before an incident opens. The organization default asks for 2 regions and 2 consecutive checks. A monitor can carry its own rule with count or percent, consecutive checks, and a minimum duration.
Plans and limits
- Shortest interval
- 300 s on Free, 60 s on Pulse, 30 s on Sentinel, 15 s on Command, and 10 s on Enterprise. The web form offers 30 s, 1 min, 5 min, 15 min, and 1 h. The 15 s and 10 s floors are reachable only through MCP.
- Regions
- 2 of 6 on Free, 3 of 6 on Pulse, and all 6 from Sentinel.
- Monitors
- 10 on Free, 50 on Pulse, 150 on Sentinel, 500 on Command, and a custom quota on Enterprise. The eleven probe types share this quota. Heartbeat and agent monitors draw on their own quotas.
From the pipeline or an agent
The same config works in the deploy step, in an MCP client such as Claude Code, and in the form above. create_monitor needs an organization-wide API key. If you omit regions, the plan picks its default.
{
  "name": "Mail relay",
  "type": "smtp",
  "interval_seconds": 60,
  "config": {
    "host": "mail.example.com",
    "port": 587,
    "tls_cert": { "enabled": true, "warn_days": 21 }
  }
}
Every interface, with its boundary
Limits
- No authentication, no message sent, and no MAIL FROM or RCPT TO. The check proves that the server answers, not that it delivers.
- The liveness probe reads only the first line of the EHLO answer. The extensions the server advertises are not evaluated.
- A monitor created without a port checks port 25, not 587.
- SPF and DMARC of the domain are not read here. The DNS hygiene check covers them.
- Targets on private, loopback, link-local, and cloud metadata addresses are refused.
- Not every region probes IPv6, so selecting
ipv6restricts the usable regions. The form offers IPv6 only when the host resolves to an AAAA record or is an IPv6 literal.